
AnalysisEU regulation
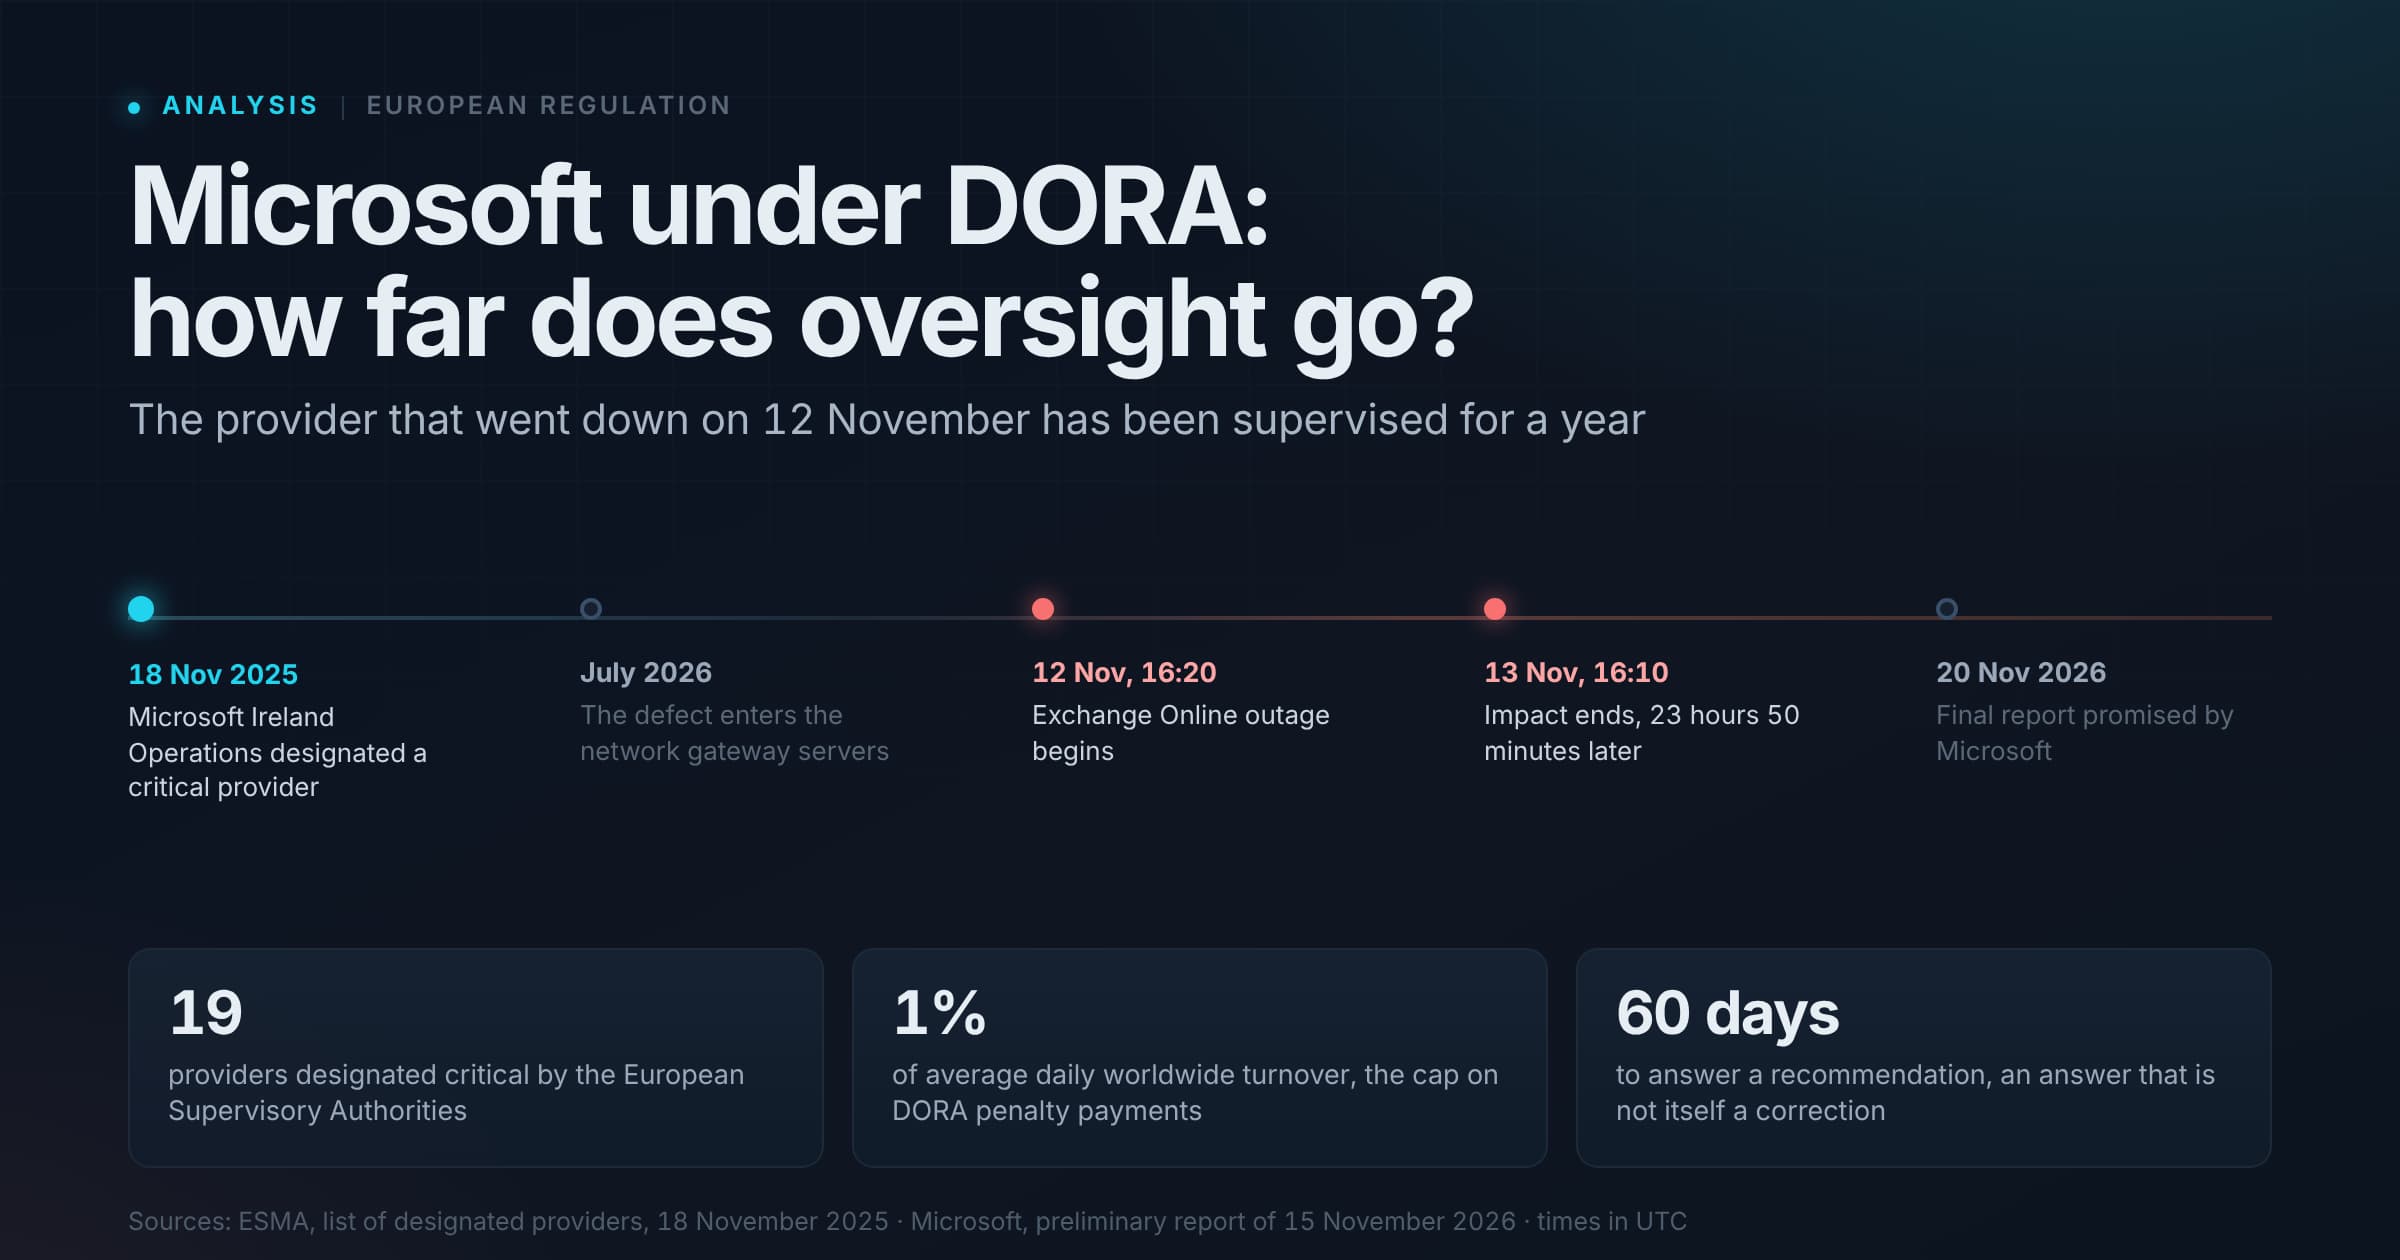
Microsoft under DORA: how far does European oversight go?
Microsoft Ireland Operations has been under direct European oversight since 18 November 2025. The November outage shows how far that power actually goes.
A full stack and DevOps engineer at CNRS - Sorbonne Université, Brahim Lamjarad spends his days deploying and maintaining the kind of systems the texts he analyses are aimed at. Master's in information systems, and a spell at Enedis on GDPR compliance and sensitive data anonymisation. Through CyberSphere he covers threats, cyber geopolitics and European regulation, picking up where most coverage stops: what actually changes, and for whom.
Microsoft Ireland Operations has been under direct European oversight since 18 November 2025. The November outage shows how far that power actually goes.
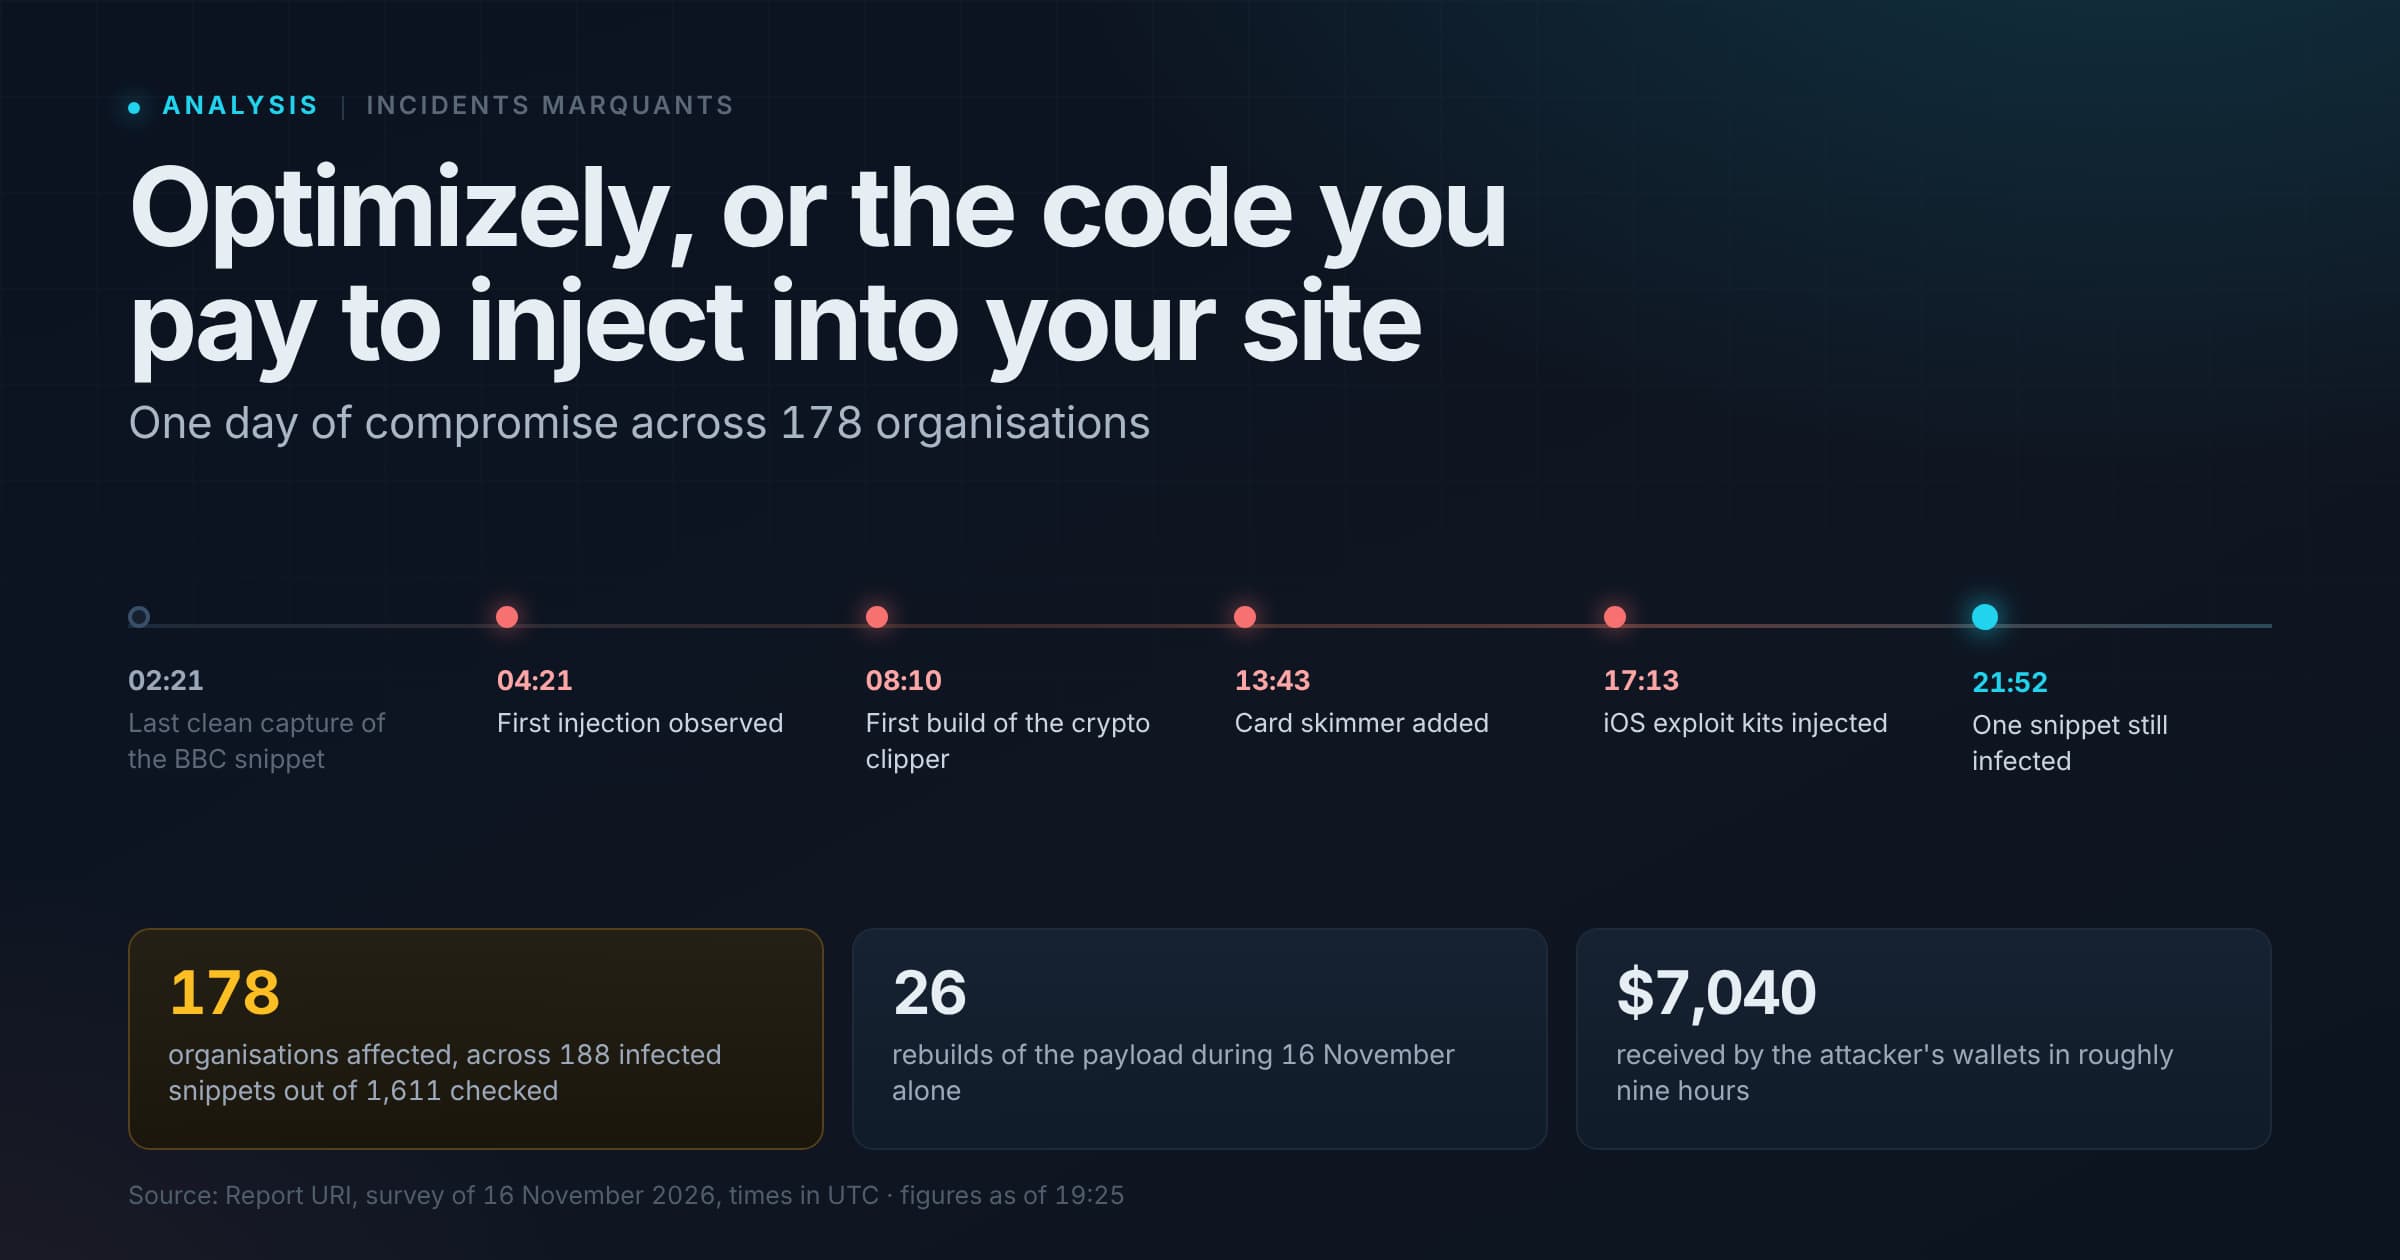
178 organisations served a card skimmer through Optimizely. The attacker subverted nothing. He used exactly the function the platform exists to provide.
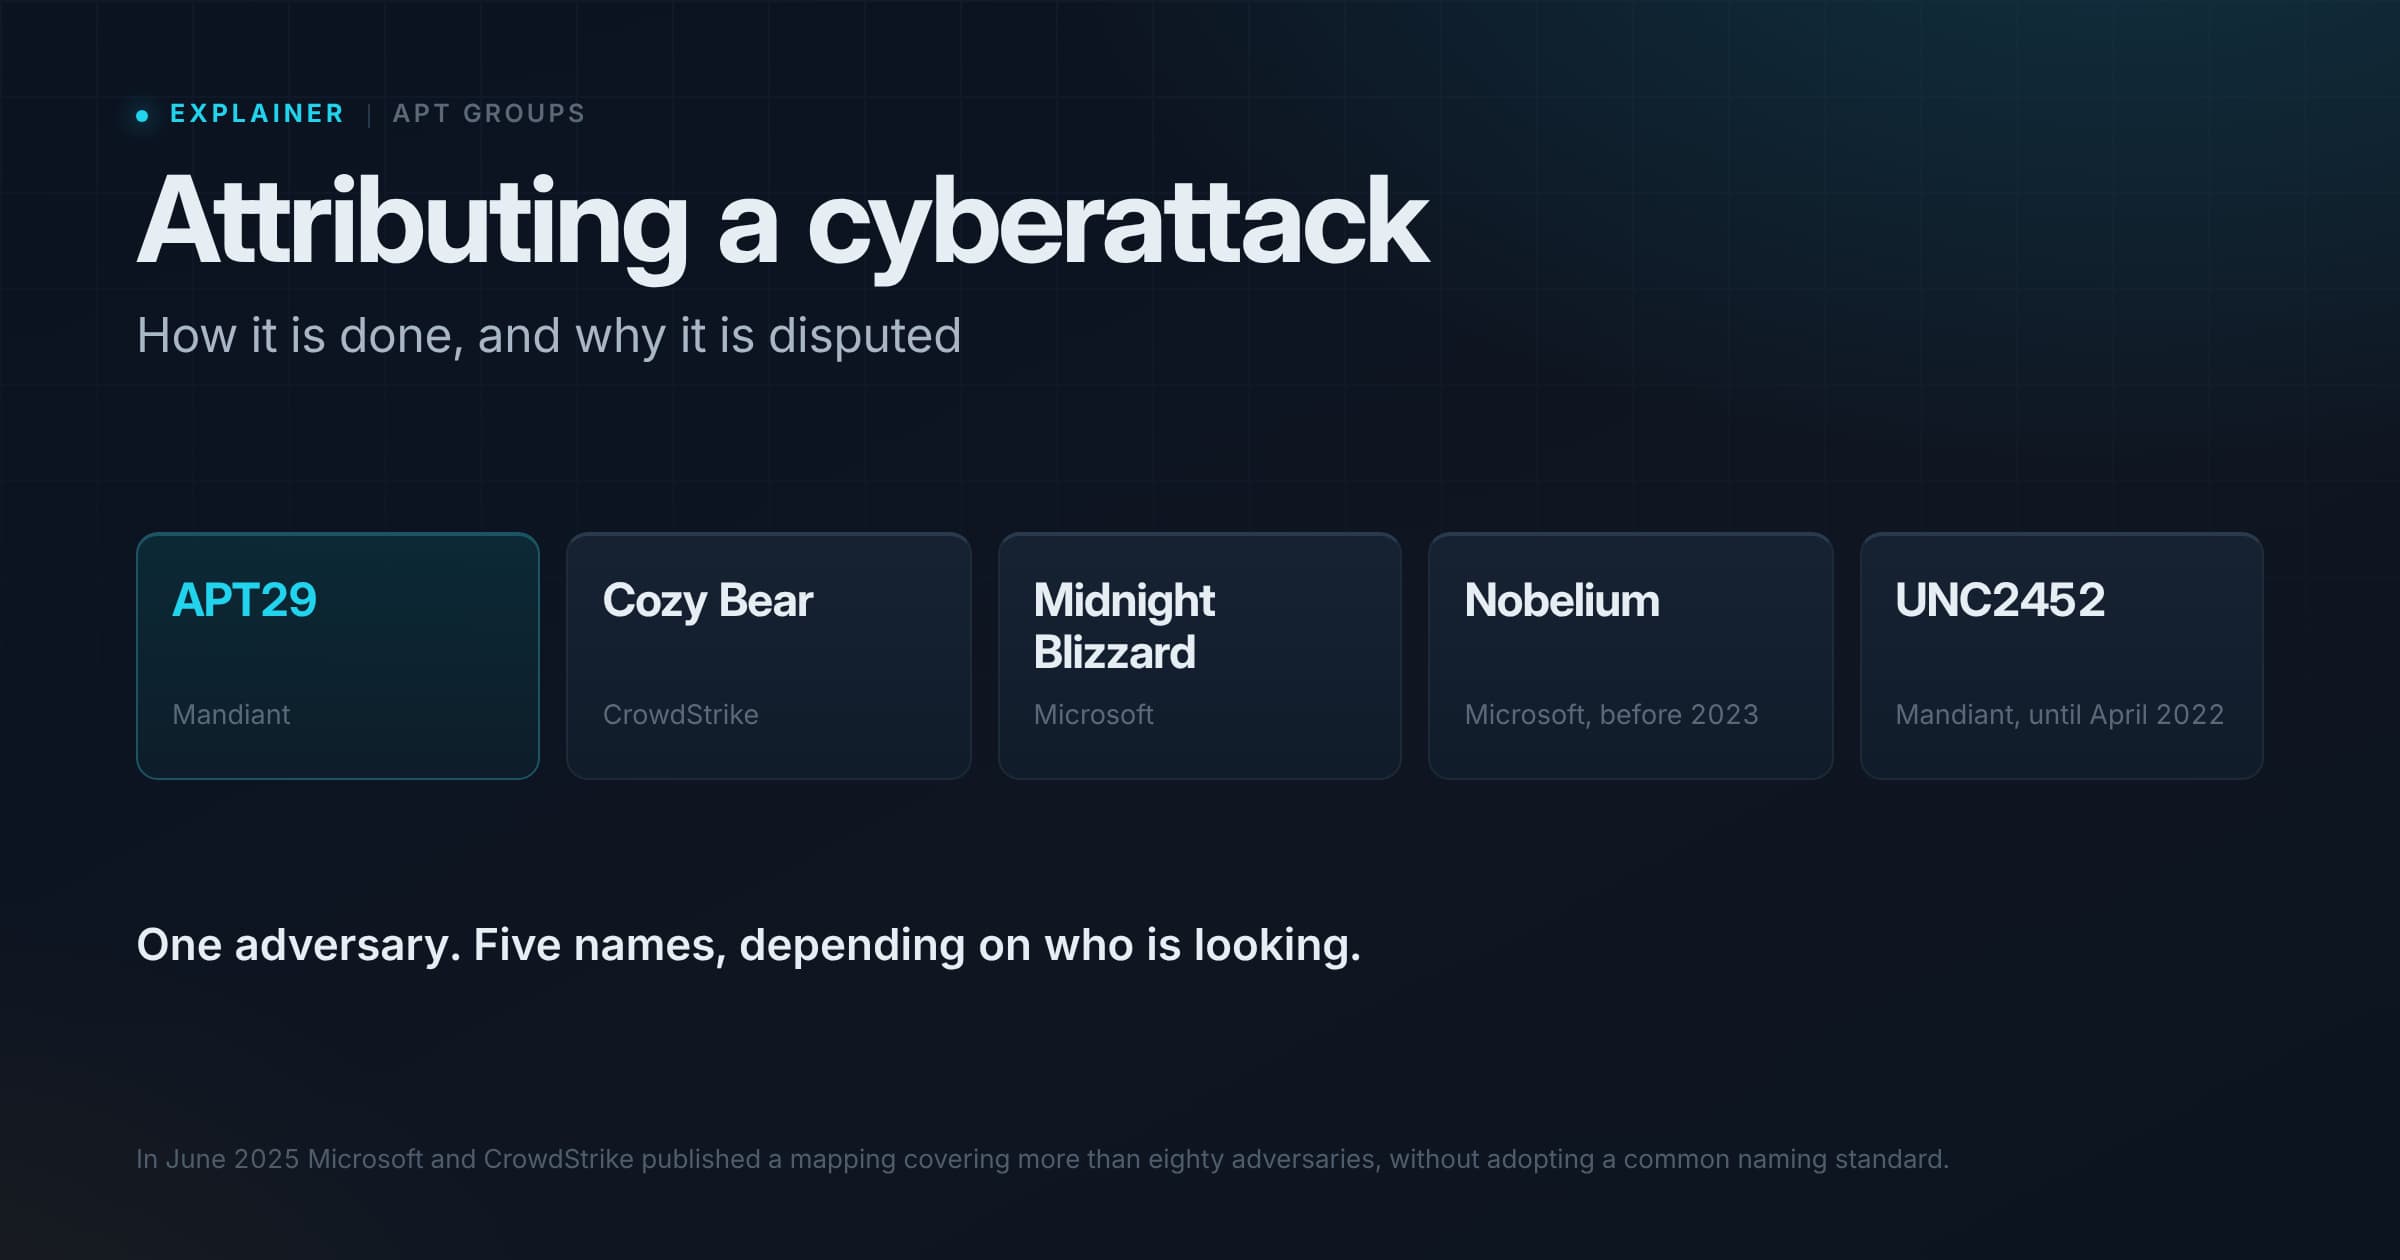
APT29, Cozy Bear, Midnight Blizzard: three of the five names one group carries. What technical evidence can establish, what it cannot prove, and who decides.
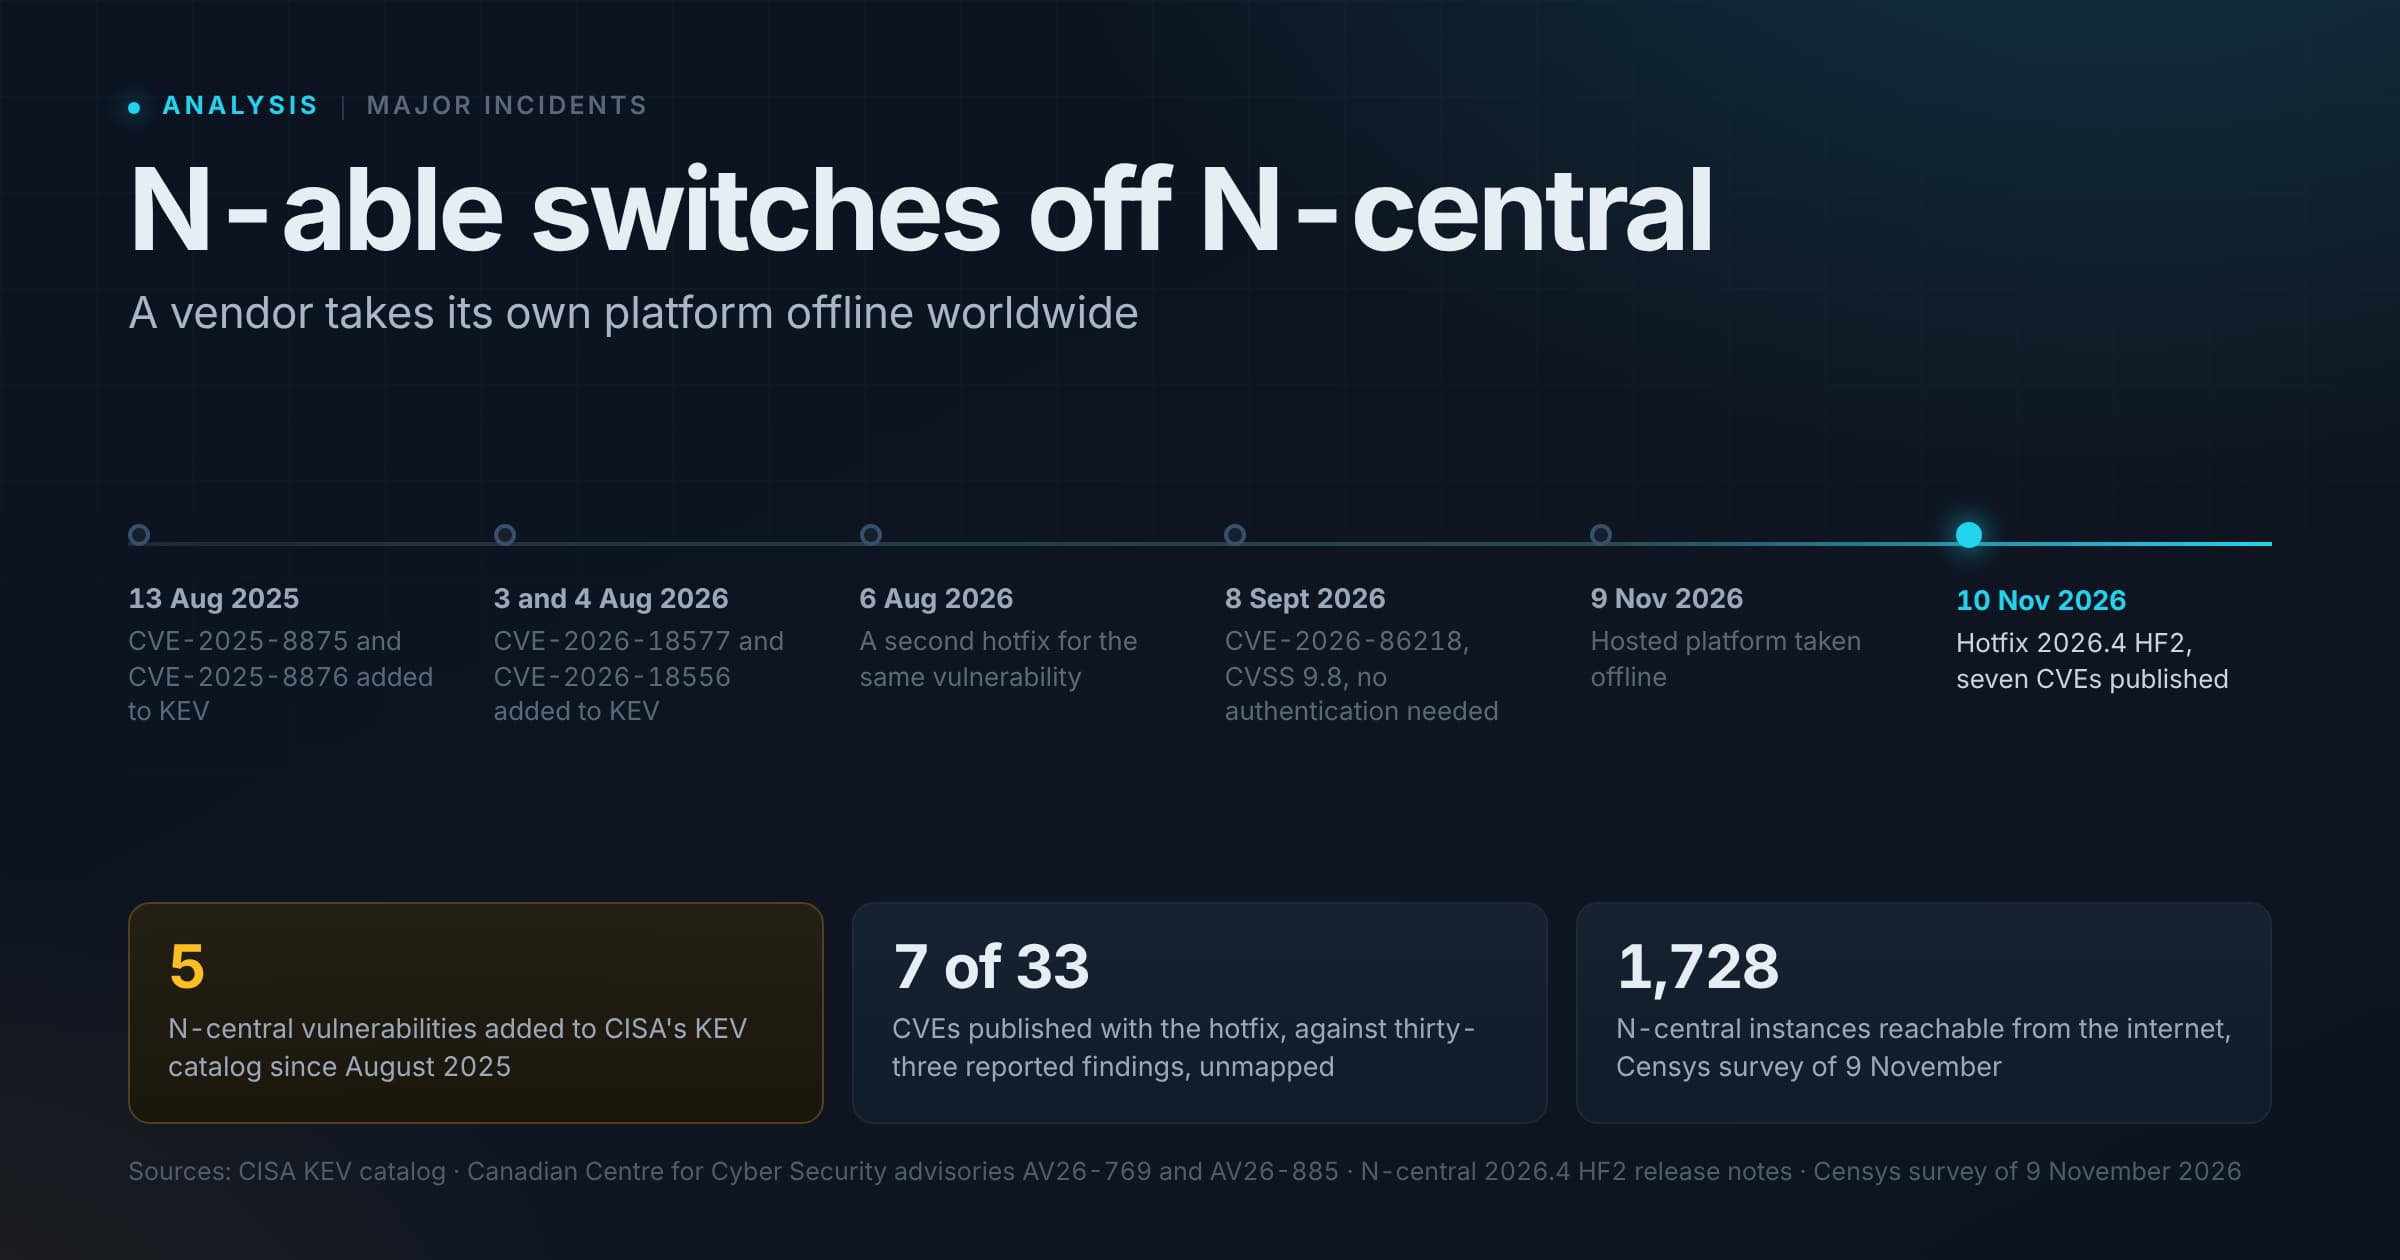
Able2Shell: seven CVEs fixed, then fresh exploit chains claimed against the hotfix. What the N-central affair says about the tools that run other people's IT.
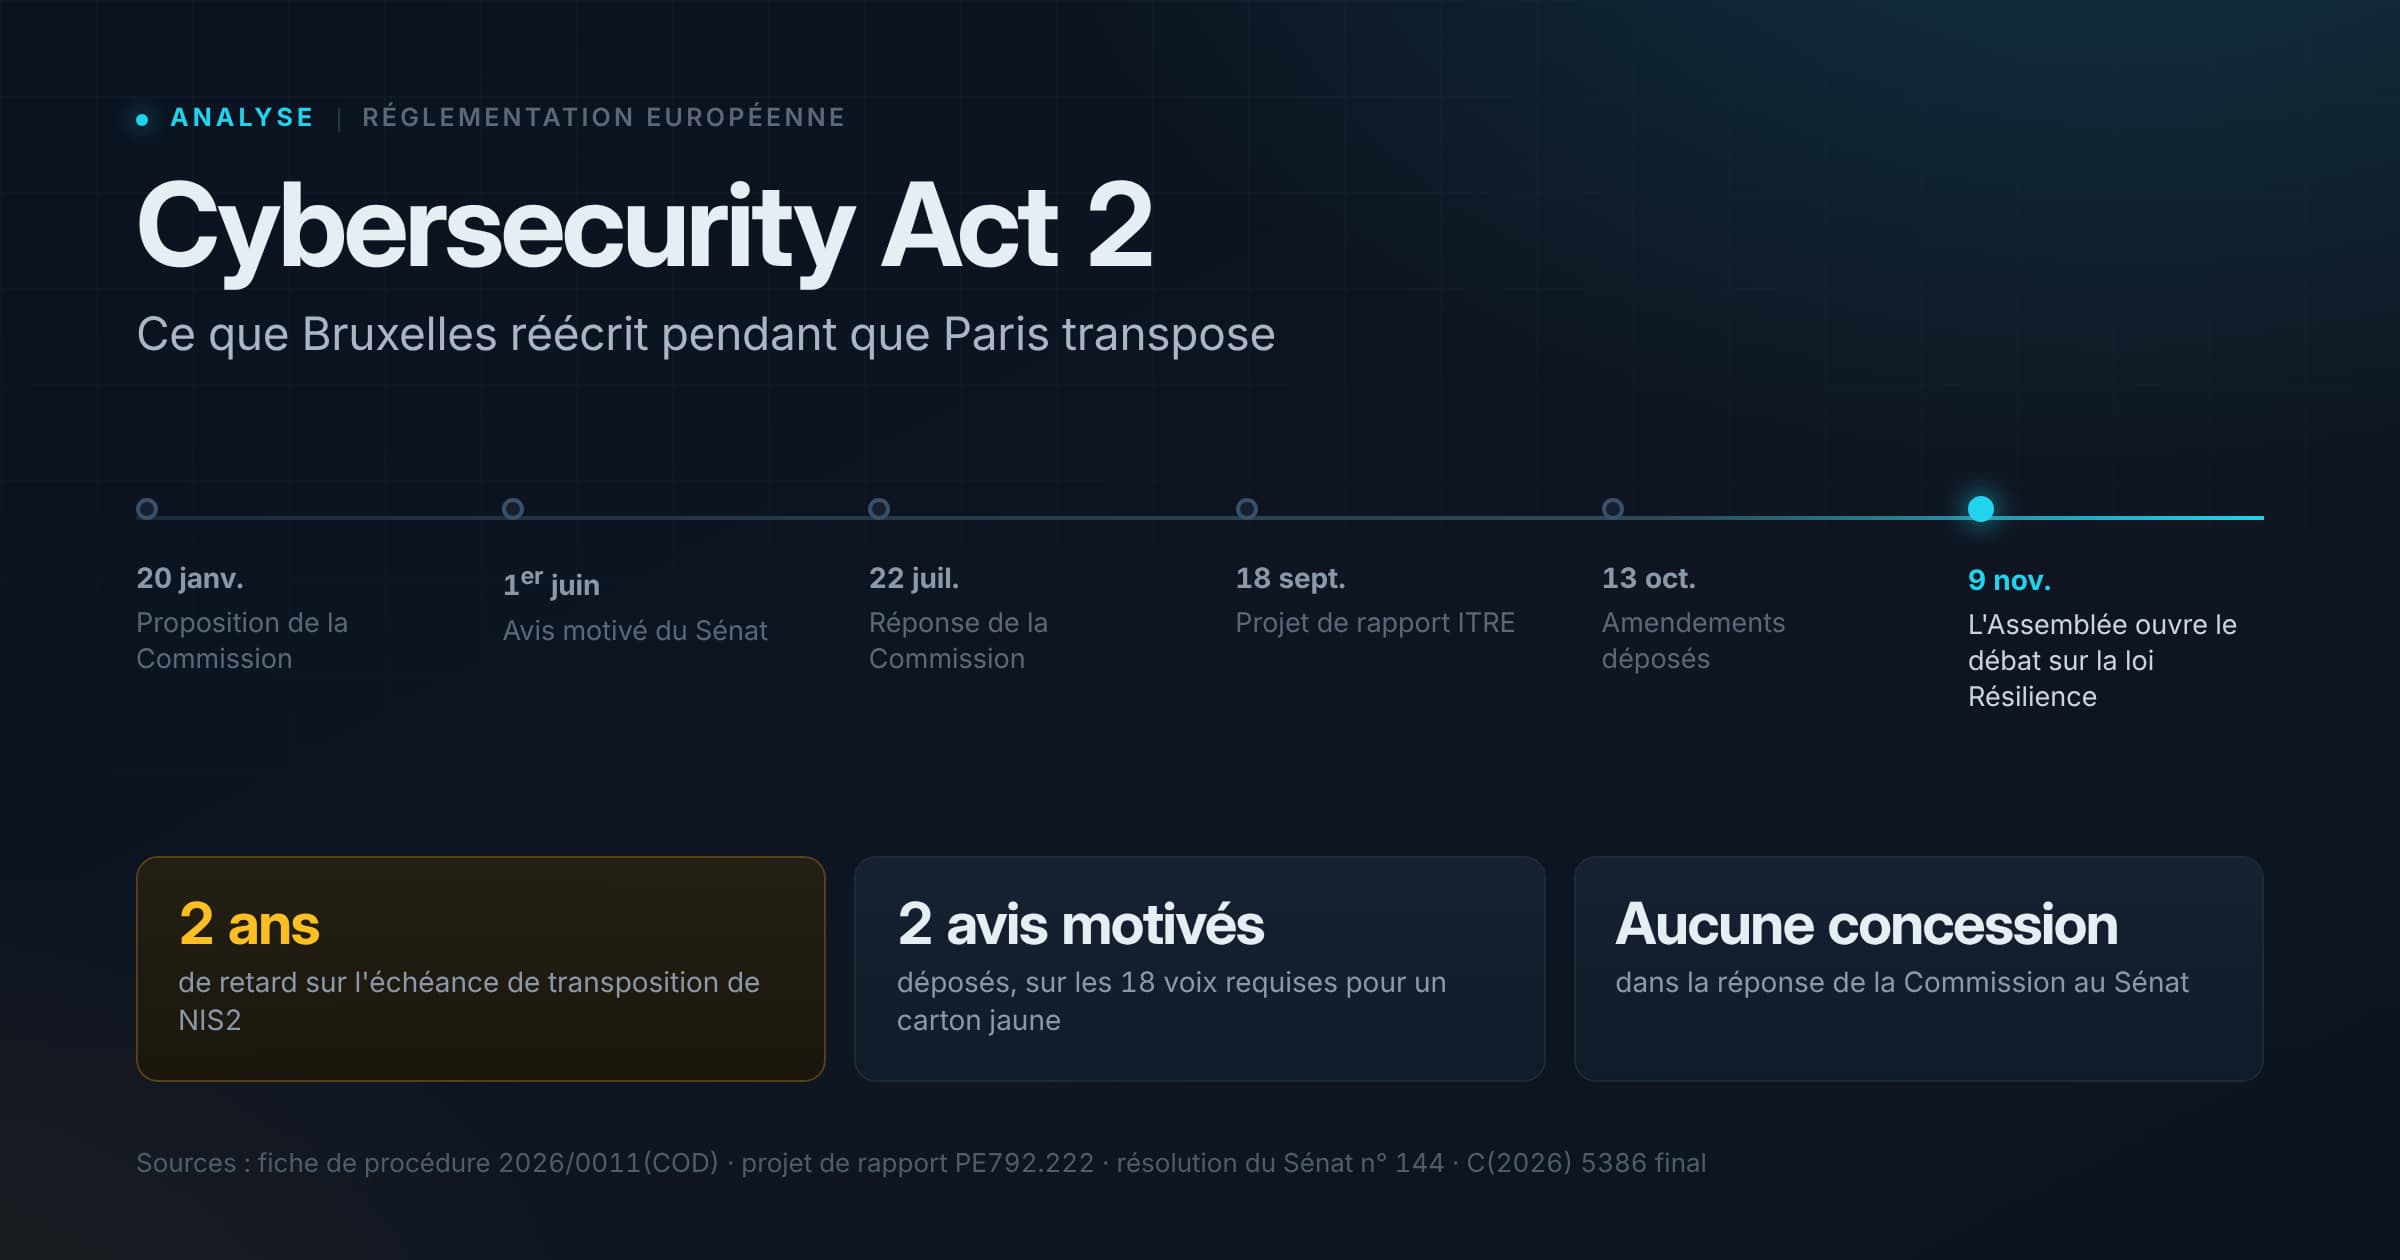
France transposes NIS2 two years late while Brussels prepares its revision. The Senate challenged the package on subsidiarity; the Commission amended nothing.
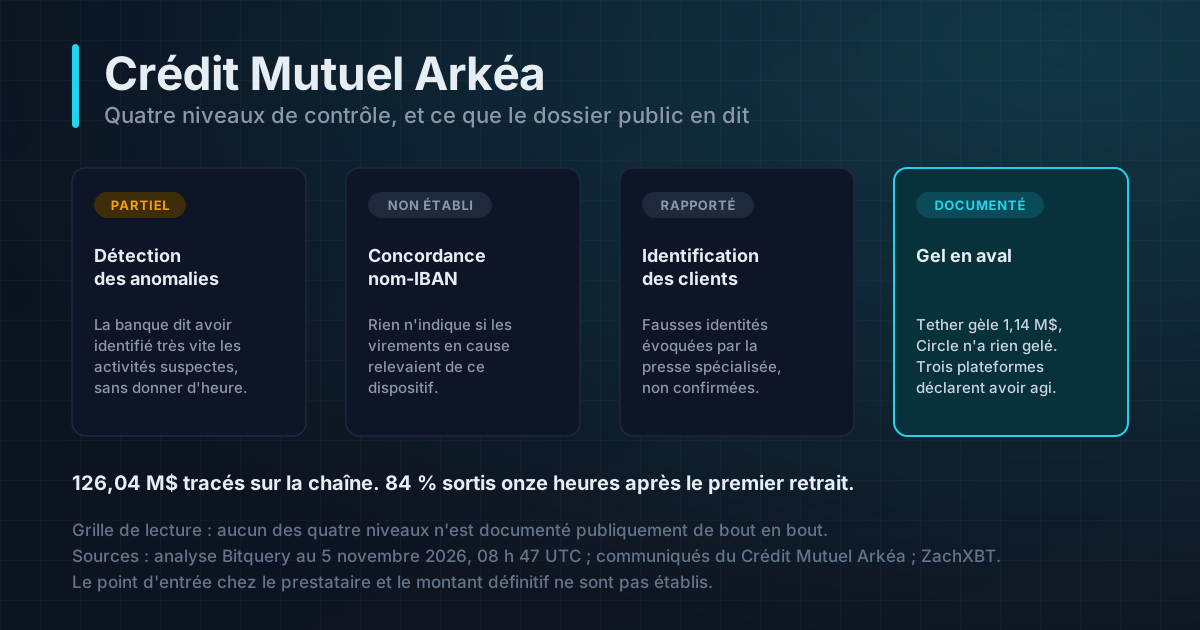
Four levels of control sit between a bank transfer and its conversion into crypto. In the Crédit Mutuel Arkéa case, only one produced a documented effect.
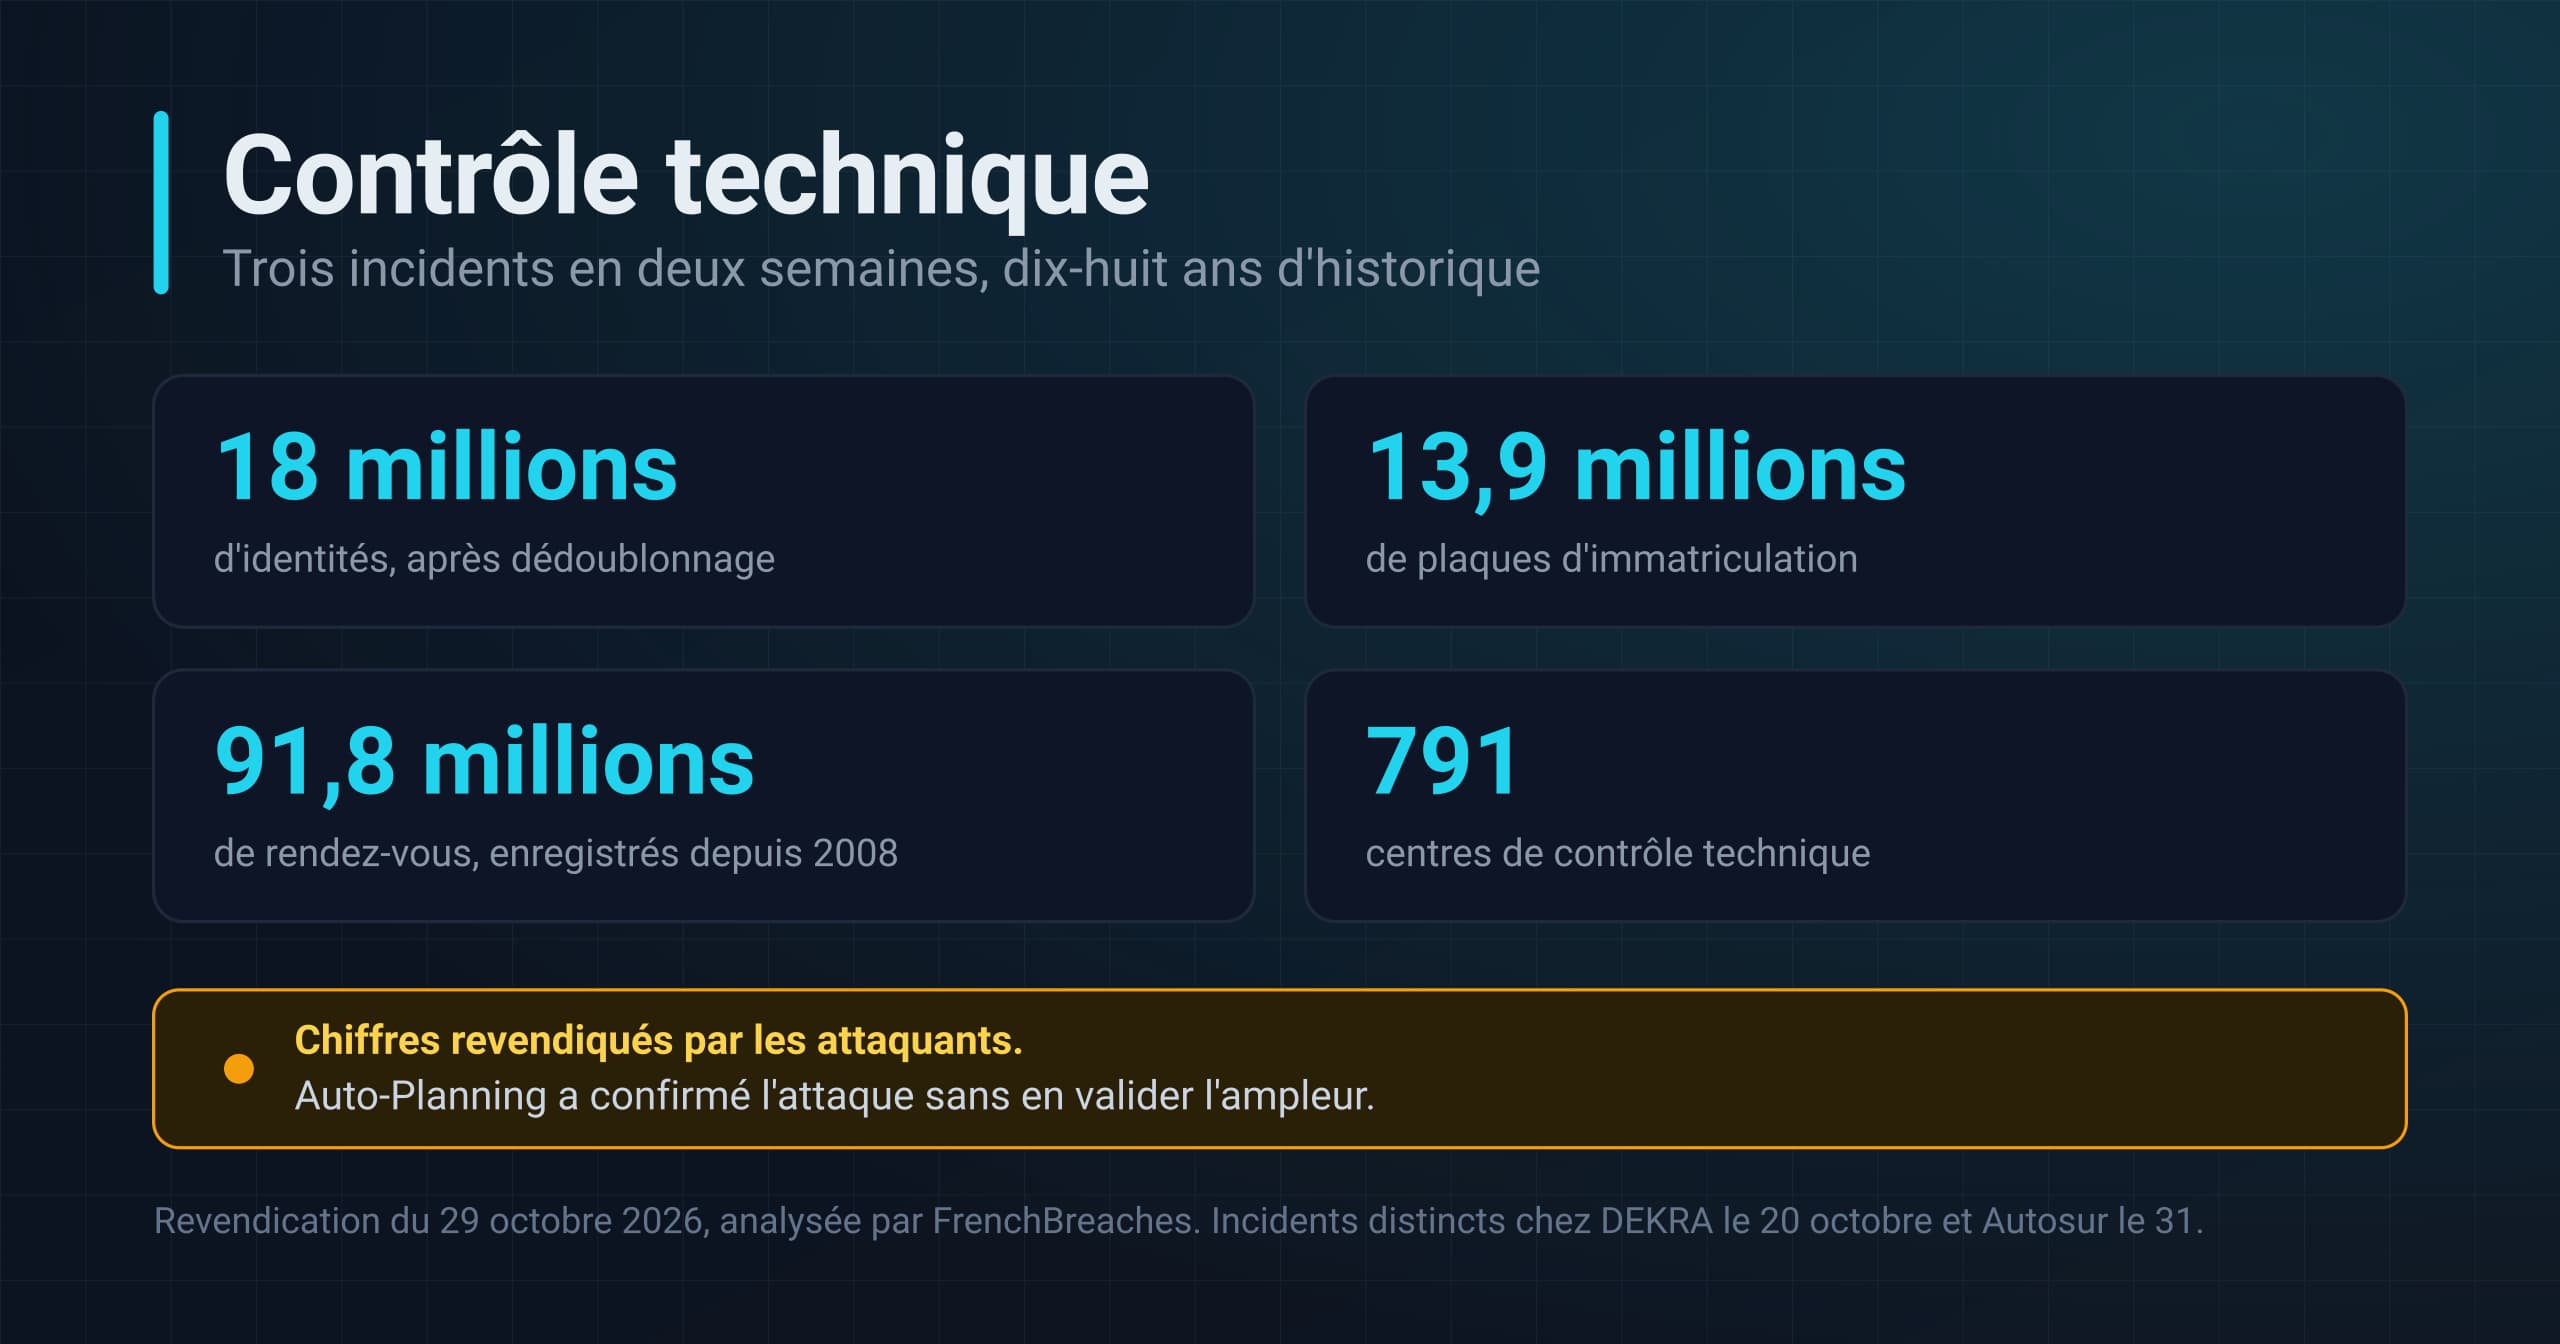
Three incidents in two weeks at vehicle inspection suppliers, eighteen years of records, and no simple way to find out whether you are among the affected.
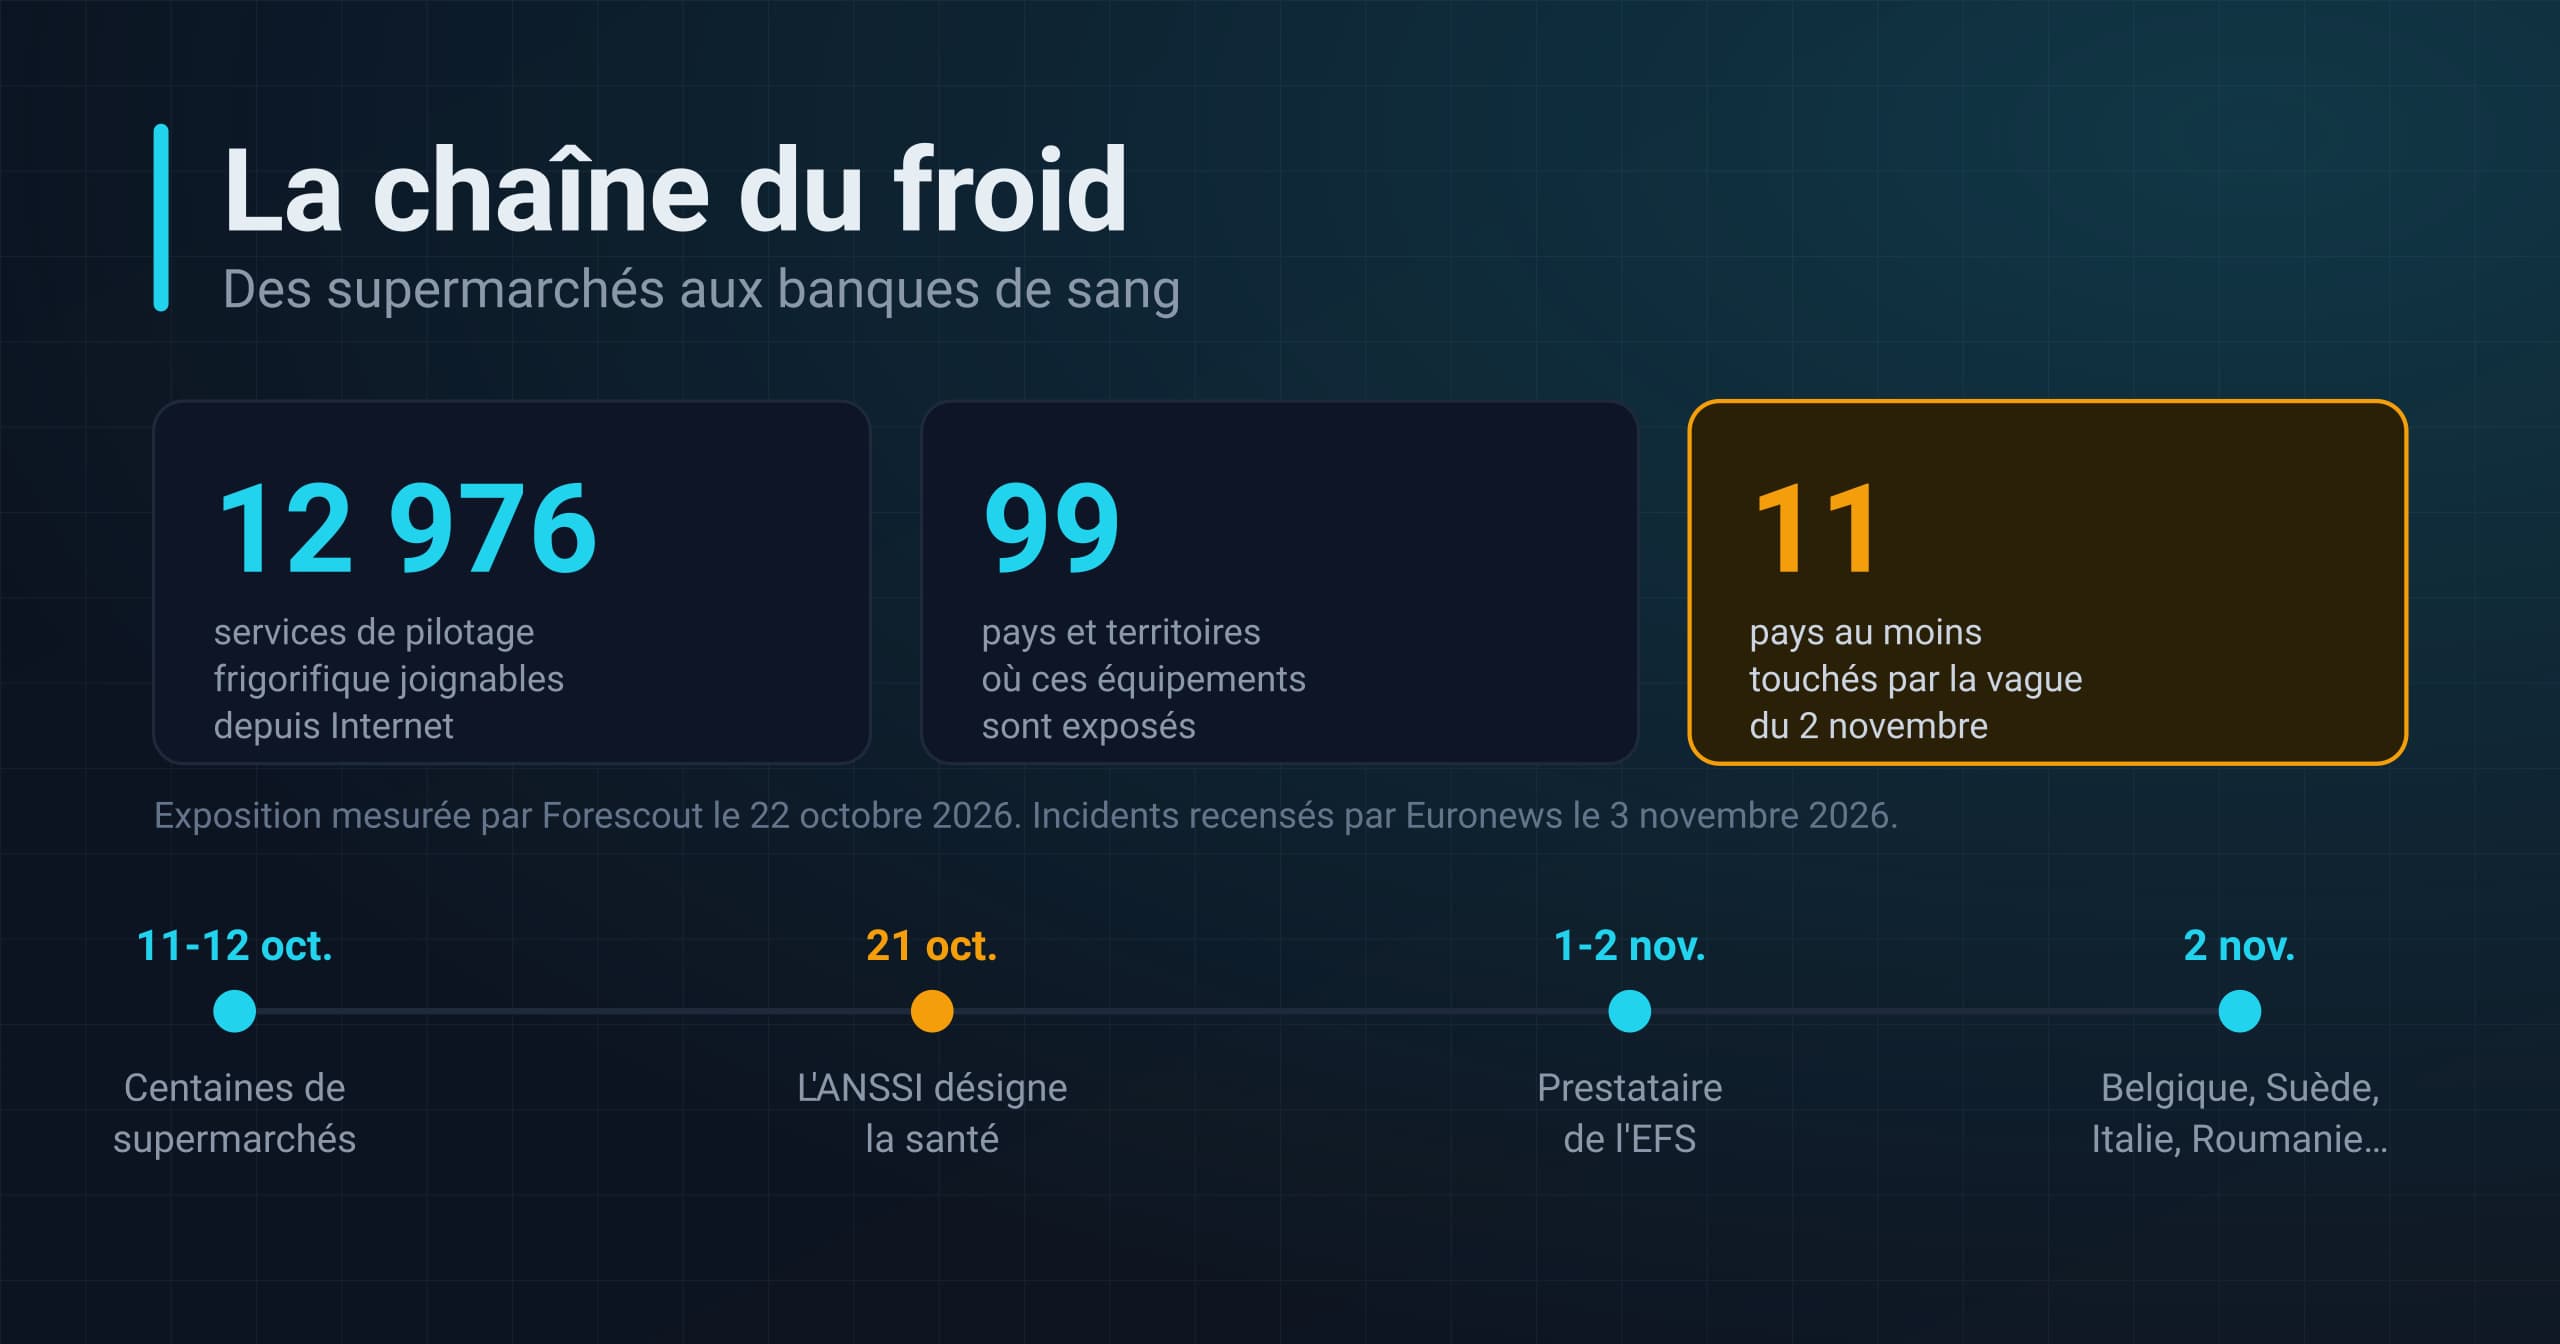
Hundreds of French supermarkets in October, eleven countries in November, then the blood service. What the campaign against connected cold storage shows.
An introduction to the blog and its editorial line: understanding cybersecurity through analysis — threats, geopolitics, regulation and strategy.